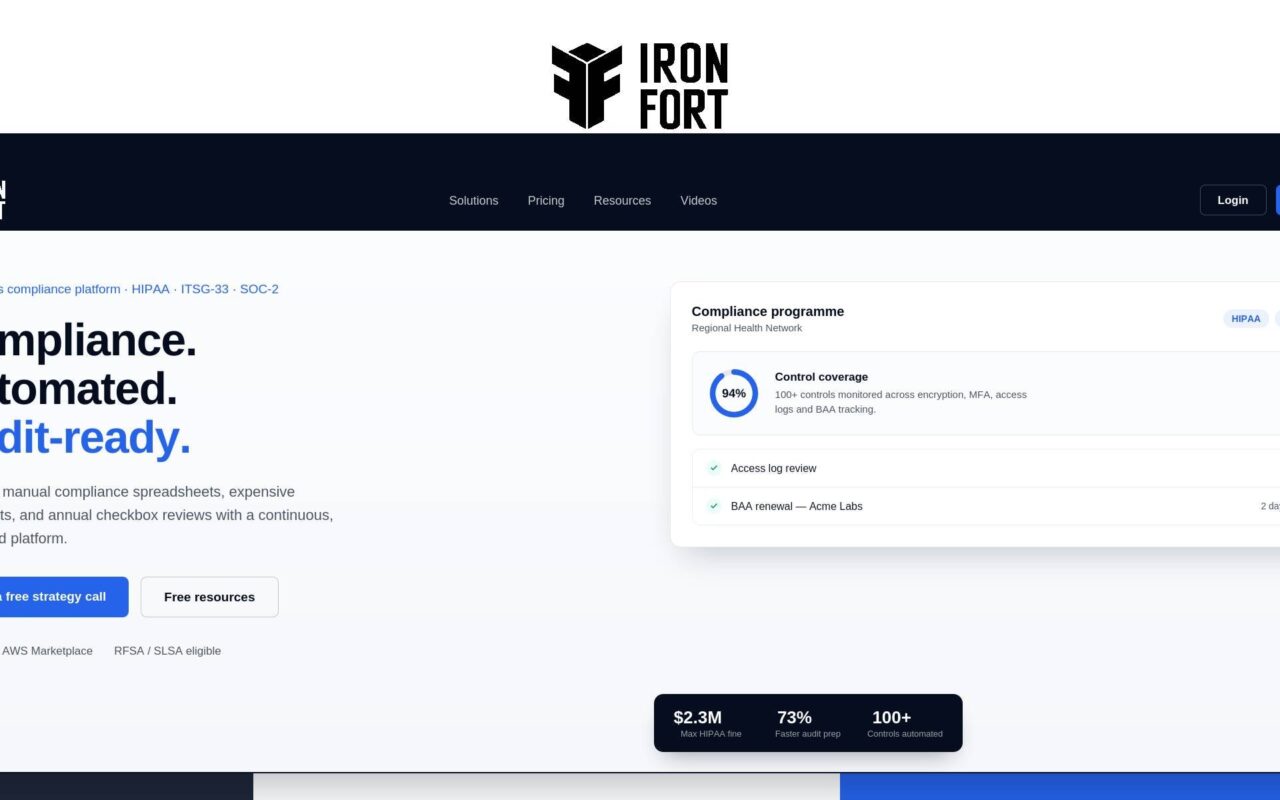
Compliance audits usually mean months of spreadsheets, screenshots and consultant invoices. Iron Fort replaces that with continuous monitoring: it connects to your stack, gathers timestamped evidence automatically and keeps a live view of which controls are passing and which need work.
An AI risk analyzer ranks control gaps by severity, so your team fixes what matters first. Policy reviews compare your documents against SOC 2, HIPAA and ITSG-33 requirements, and shared controls are mapped across frameworks so you never do the same work twice. When the auditor arrives, you export an organized audit package on demand.
Best for
SaaS startups preparing for their first SOC 2, healthcare teams handling HIPAA, and Canadian public-sector suppliers working with ITSG-33.
No reviews yet. Be the first to review this deal.